






Ravencoin KAWPOW bug: a header picking its own PoW check
In August 2026 Ravencoin rolled its chain back by about three days. The cause was one field in the KAWPOW block header. A block could state a false height there and skip the costly part of its proof of work check.
If you mine RVN through a pool, you need to change nothing. If you run a node, run version 4.8.0. All code quoted here is read from Ravencoin's own consensus source. Where an announcement says more than the source shows, we say so instead of guessing.
Ravencoin KAWPOW bug in short
- A KAWPOW header states its own height in a field called nHeight.
- Below the last checkpoint, the node ran a cheap check that trusted the mix_hash in the header.
- The node never compared nHeight with the block's real place in the chain.
- So a block at 4,487,776 could claim a height under 2,383,550 and skip the memory-hard work.
- Forged blocks met the same difficulty target, but each guess cost almost nothing.
- 2Miners shipped hotfix 4.6.1.1-hf1 on 10 August. Version 4.8.0 is the release to run.
- Pools rebuilt the chain from block 4,487,775, so about three days of blocks were discarded.
What is in a KAWPOW block header?
KAWPOW is Ravencoin's proof of work. It is a variant of ProgPoW, and the chain moved to it in May 2020. The goal was to keep the coin on ordinary GPUs. That move changed the block header.
Before activation, the header ends with the usual 32-bit nonce of every Bitcoin-derived chain. A nonce is the number a miner changes on each guess. After activation, the serializer writes three fields into that slot, in this order:
- First, nHeight: the height the block claims for itself.
- Then nNonce64: a wider nonce.
- Last, mix_hash: the result of the memory-hard part of the work. It gives a verifier a value to check, so it need not repeat the work from nothing.
nHeight is the field that matters. A block's real place is fixed by hashPrevBlock, the hash of the block it builds on. You cannot fake that and still attach to the tip, the newest end of the chain.
nHeight is a second, writable copy of the same fact. A copy is only worth as much as the check that compares it with the original.
What are the two KAWPOW hash functions?
Ravencoin's hash.cpp defines two KAWPOW entry points. Their signatures tell most of the story:
- uint256 KAWPOWHash(const CBlockHeader& blockHeader, uint256& mix_hash)
- uint256 KAWPOWHash_OnlyMix(const CBlockHeader& blockHeader)
The first function hands back a mix_hash, because it produces one. It picks the dataset with ethash::get_epoch_number(blockHeader.nHeight). It builds that epoch's context if it does not hold it yet, then runs progpow::hash over it.
The mix it returns is a by-product of doing the work. This is the memory-hard path. Memory hardness is the whole reason KAWPOW exists rather than a plain hash.
The second function produces nothing. It uses the mix already in the header, through progpow::hash_no_verify(blockHeader.nHeight, header_hash, to_hash256(blockHeader.mix_hash.GetHex()), blockHeader.nNonce64).
The upstream library named it hash_no_verify, and the name is exact. It runs the final mixing step over a value it was handed. It never builds the dataset, so it never proves that value came from real work.
Neither function is a mistake. A checkpoint is a block hash written into the node's code as known good. A node syncing millions of blocks a checkpoint already settled should not rebuild a multi-gigabyte dataset per epoch. The only question is which blocks may take the cheap path.
How did a block choose its own proof of work check?
CheckBlockHeader in validation.cpp answers that question. The comment above it states the intent plainly: "If we are checking a KAWPOW block below a know checkpoint height. We can validate the proof of work using the mix_hash".
The intent is correct. But the code gates on block.nHeight <= (uint32_t)pcheckpoint->nHeight. And block.nHeight is the number the block wrote about itself.
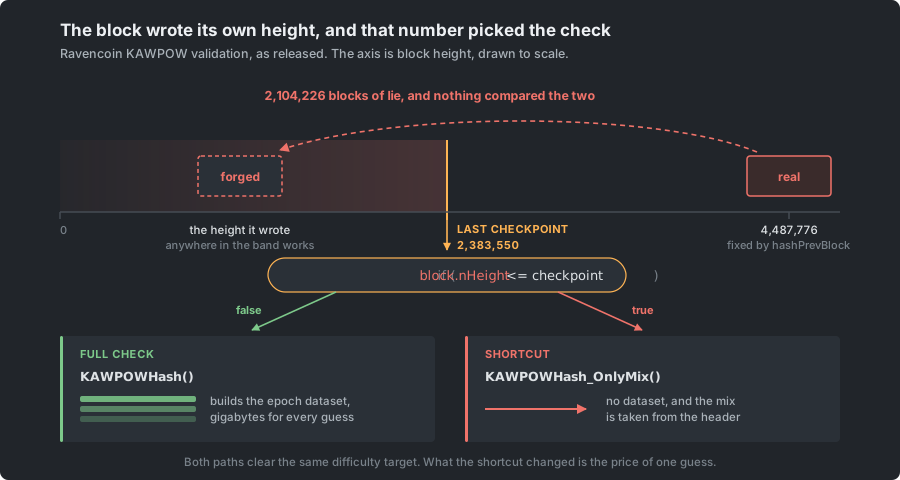
The next line calls the generic CheckProofOfWork(uint256 hash, unsigned int nBits, const Consensus::Params&). It receives a finished hash and a target and compares them. It has no mix, no nonce and no header, so it cannot know which function made the hash.
For a KAWPOW block, CBlockHeader::GetHash() returns KAWPOWHash_OnlyMix(*this). So the hash it checks is the cheap one. Nothing on that path asked where the mix came from. Nothing compared the declared height with the block's real place.
How low was low enough? The highest checkpoint in the released mainnet parameters is 2,383,550. The first forged block sat at 4,487,776. Its header claimed a place about 2.1 million blocks behind its real one, and the branch it chose never noticed.
Did the bug lower Ravencoin's difficulty?
No. Much of the coverage was loose on this point. The loose version makes the bug sound stranger than it is.
The nBits field, the difficulty target, is checked against what the real previous block requires. The hashPrevBlock field picks that block, and an attacker cannot fake it and still land on the tip. So a forged block had to meet the same target as an honest block mined that minute.
What changed was the price of one guess:
| Property | Honest KAWPOW block | Forged block |
|---|---|---|
| Difficulty target | Set by the real previous block | The same target |
| Work per guess | A full pass over a dataset measured in gigabytes | A header hash plus one final mixing step |
| Where mix_hash comes from | Computed from the dataset | Picked freely by the attacker |
| Cost per guess | Full KAWPOW cost | Cheaper by orders of magnitude |
The memory-hard work is why KAWPOW has kept ASICs, chips built for one algorithm, off Ravencoin for six years. 2Miners described the forged results as near zero work blocks. Measured against what KAWPOW should cost, that is fair.
What happened on the Ravencoin network?
- 7 August 2026, 15:44:01 UTC: the first known invalid block, at height 4,487,776.
- 7 to 10 August: the exploit continued.
- 10 August: 2Miners released the emergency hotfix 4.6.1.1-hf1.
- 19 August: the Ravencoin project published version 4.8.0, according to 2Miners.
In one stretch of 2,089 blocks, 2Miners counted 96 affected ones. So the forged blocks were scattered through the branch, not packed into one run.
That is why the remedy had to be a reorganisation, not a surgical removal. A reorganisation, or reorg, replaces recent blocks with a competing chain.
Why did Ravencoin nodes crash and stop syncing?
For node operators, the symptom was worse than a quietly accepted bad block. Nodes crashed on these blocks, and after a restart they stopped syncing. Tron Black has since described how:
- The block index stores the height a block really sits at, not the height its header declared.
- On restart, the node rebuilds each header from the index and recomputes its hash.
- For a forged block, it now hashes the real height where the header had a false one.
- The hash no longer matches, the proof of work check fails, and LoadBlockIndexGuts aborts.
The block was accepted once and then could not be loaded. That is why the second symptom outlived the first.
Several exchanges suspended RVN deposits and withdrawals while the branch was unresolved. That is the normal, correct response to a chain whose recent history is about to change. It is not a verdict on the coin.
What does Ravencoin 4.8.0 fix?
The first fix was version 4.6.1.1-hf1 on 10 August. It came from 2Miners, a mining pool, not from the Ravencoin project. It stopped the damage for anyone who took it.
Version 4.8.0, published through the Ravencoin repository, supersedes it. Run 4.8.0 and nothing earlier. It does four things:
- It rejects blocks from 4,487,776 onward whose declared header height does not match their real place.
- It checkpoints 4,487,775 as the last clean block.
- It rebuilds corrupted chain state by itself instead of aborting.
- It adds an asset transfer overflow fix that the hotfix did not carry, plus other upstream work.
Only the first item is the repair. Once the declared height must match the real place, the gate closes. The checkpoint and the automatic rebuild are recovery.
A checkpoint is a blunt tool. It hardcodes one specific block as the correct one, and a chain wants as few of those as possible. It is here because the honest branch had to win faster than hashrate alone would make it.
The recovery point was a judgement call. Tron Black wrote that he asked the pools to consider a more recent cut. That would have made the reorg shallower, with the forged blocks handled one by one.
The pools declined and took the cleanest line. In proof of work, that argument settles itself. A history the honest majority of hashrate refuses loses, and the two largest pools together held that majority.
What does a three-day reorg mean for RVN holders?
Vulnerable nodes accepted the forged blocks, so real blocks piled up on top of them. Discarding that branch means a reorg. At Ravencoin's one-minute block target, 4,487,776 to the patch is about three days of blocks.
Transactions confirmed on the discarded branch stop being confirmed. Most go back to the mempool, the queue of waiting transactions, and are mined again on the surviving chain. That is not guaranteed, though.
One class cannot come back. A coinbase is the new coins a block pays its miner. A transaction that spent the coinbase of a discarded block spends coins that no longer exist on the surviving chain.
So does anything built on top of it. Those are invalid, not pending. That is why the exchange pauses were right, and why activity after 4,487,775 needed caution until one tip was settled.
Why did some old Ravencoin nodes refuse the new chain?
Ravencoin nodes carry a no long reorg rule. It stops a surprise majority attack from rewriting deep history. Most old nodes that ran without a break dropped below the peer count the rule depends on. They then accepted the longer chain, as designed.
A few did not, because they never lost enough peers. By the rules as written, nothing had been broken. The protection worked exactly as specified, on a problem it was never built for.
The split came from a validation flaw, not from a 51% attack on the majority. The rule cannot tell those apart.
What to do if you mine or run a Ravencoin node
If you mine through a pool, change nothing: no new address, no new port, no miner update. KAWPOW was never the problem. The defect was in the code deciding when to run it.
The hashrate you pointed at the old branch was real work. It landed on blocks discarded along with the forged ones among them, much as an orphan block is dropped. To estimate what your rig earns, use the mining calculator.
If you run your own node, follow these steps:
- Stop the node.
- Replace the binary with version 4.8.0, not an earlier release that fixed only part of this.
- Start the node again. There is no reindex to run and no manual step.
- Expect a quick restart if you come from the hotfix.
- From unpatched software, expect several hours of replay and rebuild on ordinary hardware.
- Read bad-blk-height errors during that time as the patch working, not as a fault.
- Check the hash of block 4,494,143. On the canonical chain it ends in 4c67d6a4.
Do that last check rather than assume. The independent Ravencoin explorers all showed that same chain when the project called the network recovered.
Why did audits miss the Ravencoin KAWPOW bug?
Strip away the details and a common shape is left. A value from outside decided how carefully that same value would be examined. The header stated its own height, and the node used it to pick the check the header had to pass.
The fix is not complicated, and the patch is essentially one line of it. Compare the declared height with the block's real place before it decides anything.
The shortcut was written for blocks that are already trusted. Under that assumption, the gate reads as a fact, not a question someone could answer dishonestly. That stops once an untrusted block can fill the field in, and nothing in the code marked when that changed.
Ravencoin has had professional security audits of its code. They did not catch this flaw or the asset overflow fixed alongside it. Tron Black has written that he strongly suspects a frontier AI model security review surfaced both.
Whatever the tooling, it fits the shape. The flaw is invisible while you read the shortcut on its own terms. It appears once you ask who gets to fill in the field the shortcut trusts.
Who fixed the Ravencoin chain, and in what order?
A mining pool read the validation path and shipped an emergency binary within three days. The two largest pools then mined a chain that threw away the whole attack window. They were asked to take the shallower cut and declined.
The project followed with the release that supersedes the hotfix and fixes more. What settled the split was neither announcement. It was the weight of real work on one side, which is decentralisation doing its job.
Was the KAWPOW algorithm broken?
No. KAWPOW did what it was designed to do. The flaw was in the node code that chose when to run the full check.
Which Ravencoin version should I run?
Version 4.8.0. Earlier releases, including the 4.6.1.1-hf1 hotfix, fixed only part of the problem.
Do I need to change anything to mine RVN on a pool?
No. Keep the same address, port and miner software.
Did the forged blocks have a lower difficulty?
No. They met the same target as honest blocks. Each guess was simply far cheaper, because it skipped the memory-hard work.
How do I check my node is on the right Ravencoin chain?
Look up the hash of block 4,494,143. On the canonical chain it ends in 4c67d6a4.
Why did some of my RVN transactions disappear?
The reorg discarded about three days of blocks. Most transactions are mined again, but ones built on a discarded block's coinbase cannot return.
Where these facts come from
The header layout, the two hash functions, the epoch choice and the validation branch with its comment are read from Ravencoin's source. The files are src/primitives/block.h, src/primitives/block.cpp, src/hash.cpp, src/hash.h, src/pow.h and src/validation.cpp.
You can read validation.cpp in Ravencoin 4.8.0 and hash.cpp in Ravencoin 4.8.0 yourself. The checkpoint list is in chainparams.cpp in Ravencoin 4.8.0. Before 4.8.0, its highest mainnet checkpoint was 2,383,550.
The first invalid height and its timestamp come from the Ravencoin project's own network notice. Tron Black's account for the Ravencoin project is the source of:
- The block index crash path and the coinbase transactions that cannot return.
- The no long reorg behaviour and the declined shallower recovery point.
- The audit and AI review remarks.
- What 4.8.0 contains, and the 4,494,143 check.
The hotfix version, the 96 affected blocks within 2,089 and the 4.8.0 date come from the 2Miners August 2026 report. We read the source files and that report on 5 November 2026. Anything the sources do not state is left out.